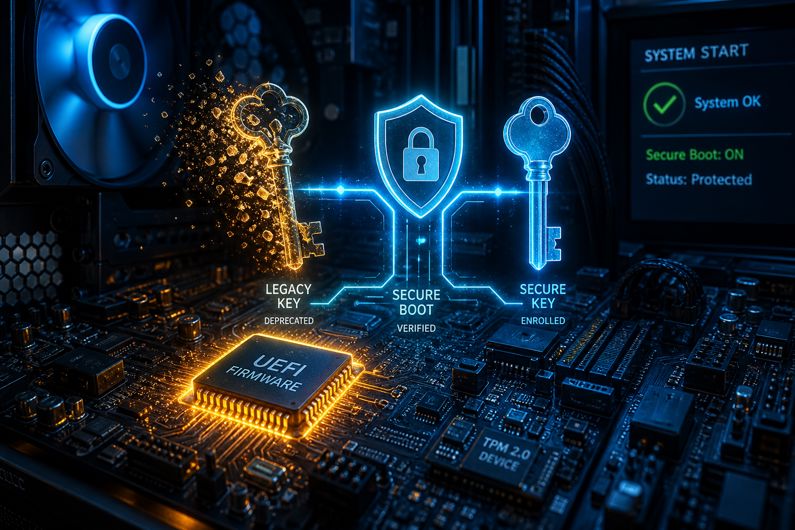
A certificate that has helped Windows PCs verify their startup software for roughly 15 years reached its scheduled expiration on October 19, 2026. The milestone brings renewed attention to Microsoft’s transition from its original 2011 Secure Boot certificates to a newer generation issued in 2023.
The affected certificate, Microsoft Windows Production PCA 2011, is part of the trust infrastructure used to authenticate Windows boot components. Its expiration is not a Windows support deadline, a newly disclosed vulnerability, or a signal that every affected computer will suddenly stop starting. It does, however, make the state of a device’s Secure Boot certificate updates an increasingly relevant security question.
For businesses, the practical issue is whether their computers can continue accepting newer, trusted boot components as Microsoft updates the startup environment. For individual users, the priority is less dramatic: keep Windows and manufacturer-provided firmware current, and do not assume that a computer starting normally proves the transition is complete.
A security transition below the operating system
Secure Boot operates through a computer’s UEFI firmware, before Windows takes control. It checks the signatures of startup software against trusted certificates and other authorization data, helping prevent unauthorized components from inserting themselves into the boot process.
That position matters. Malware that compromises startup components can operate beneath many of the protections users associate with an antivirus scan or a signed-in Windows session. Secure Boot is not a complete defense against every such attack, but it provides an important foundation for trusting what runs first.
The certificates behind that foundation have finite lifetimes. Microsoft’s original deployment relied on certificates issued in 2011, and several reached their scheduled expiration dates during 2026:
- Microsoft Corporation KEK CA 2011: June 24, 2026. This certificate is associated with authorizing updates to Secure Boot signature databases.
- Microsoft Corporation UEFI CA 2011: June 27, 2026. This certificate has been used to establish trust in third-party UEFI components, including certain non-Windows bootloaders.
- Microsoft Windows Production PCA 2011: October 19, 2026. This certificate has been used to verify Windows boot components.
These are related parts of the same trust system, but they are not interchangeable. Updating a certificate used to authorize database changes is a different operation from establishing trust in a newly signed Windows boot manager.
Microsoft’s replacement infrastructure includes Windows UEFI CA 2023 and newer certificates for other Secure Boot roles. The migration therefore involves more than replacing a single file inside Windows: the firmware’s trust data and the software it authenticates must remain compatible throughout the change.
Expiration does not mean an instant boot failure
The most consequential distinction is between continuing to boot existing software and remaining ready for future boot-security updates.
A PC using older Secure Boot certificates can continue starting after those certificates expire. The deadline should not be understood like an expired website certificate that immediately produces a visible browser warning. Existing startup behavior does not necessarily change simply because the calendar passes the certificate’s expiration date.
The concern is what happens next. Devices that have not received the appropriate replacement certificates can be unable to take advantage of future protections for the early boot process. A functioning desktop is therefore not sufficient evidence that a machine is prepared for the newer signing infrastructure.
Equally, the expiration date alone does not prove that a particular machine is exposed to an active exploit. Establishing its condition requires checking the actual update and firmware state, rather than inferring it from the age of the PC or the Windows version shown in Settings.
Why fleet readiness is harder than installing a monthly patch
On a managed corporate network, this transition crosses responsibilities that are often split between teams. Endpoint administrators oversee Windows updates, hardware teams handle firmware, and security teams set requirements for boot integrity and disk encryption.
Firmware implementation differences add another complication. A company may have thousands of computers running the same Windows release while using several generations of motherboards, firmware revisions, and factory-provisioned Secure Boot databases. Their readiness cannot safely be reduced to one operating-system inventory field.
Windows Update is an important delivery mechanism, but administrators should verify the outcome rather than treat an installed update as universal proof that every underlying change succeeded. Microsoft’s deployment guidance and each manufacturer’s compatibility information are more useful than a blanket assumption about an entire device family.
The transition also has implications for Windows recovery media. A device’s installed operating system is only one route through its startup chain. Organizations may also depend on USB recovery drives, network deployment tools, or older maintenance environments. As trusted certificates and revocation policies evolve, those alternative startup paths need compatibility testing too.
Before making firmware or boot-trust changes at scale, administrators should confirm access to BitLocker recovery keys and test representative hardware. Some changes to the measured startup environment can trigger a recovery prompt. That possibility is a reason to prepare carefully, not an argument against updating.
What users and IT teams should check now
For a personally managed PC, the sensible first steps are to install applicable Windows updates, review firmware updates from the device manufacturer, and consult current Microsoft guidance for the machine’s Windows version. Downloading replacement certificate files from an unofficial source or manually altering firmware trust settings without a documented procedure introduces unnecessary risk.
For organizations, the useful deliverable is a device-level picture of Secure Boot migration readiness: which systems have the replacement trust material, which need firmware attention, and which require investigation or a supported remediation path.
Disabling Secure Boot is not a substitute for completing the transition. It removes a protection rather than renewing the trust infrastructure behind it.
The October 19 milestone makes a normally invisible dependency visible. Windows security maintenance reaches below the operating system, into firmware databases and the signatures on the first software a machine executes. The immediate question is not simply whether a PC still starts. It is whether its startup trust chain is ready for the next security update.
Source context: Microsoft’s published Secure Boot certificate-expiration schedule and its Secure Boot documentation. The dates describe certificate lifecycle milestones; update availability and deployment status must be checked for individual devices.