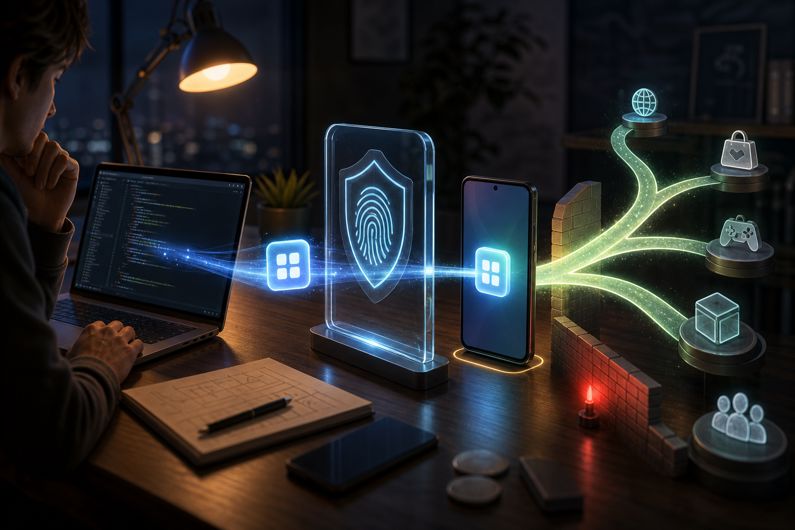
Android’s openness is facing a practical test: whether developers distributing apps outside Google Play should have to identify themselves to Google before those apps can be installed on certified devices. Google’s developer verification initiative extends identity checks beyond its own storefront, bringing independent distribution into a security framework previously associated more closely with Play.
Under the timetable Google announced in August 2025, the first regional enforcement phase was scheduled for September 2026 in Brazil, Indonesia, Singapore and Thailand, with broader expansion planned from 2027. That makes the treatment of independently distributed Android apps an immediate issue for developers, businesses and users—not simply a distant policy proposal.
Reporting scope: This article examines Google’s published verification plan and its implications. The current country-by-country enforcement status, any subsequent exceptions and changes to the rollout have not been independently verified as of October 20, 2026.
The change reaches beyond the Play Store
The central distinction is between an app’s distribution channel and the device on which it runs. An Android application can be offered through a developer’s website, an alternative marketplace or an organization’s own distribution system. Google’s plan adds a developer identity requirement at the certified-device level rather than limiting that requirement to applications listed in Google Play.
In its announced form, the policy calls for developers to verify their identities and register their apps for installation on certified Android devices in regions where the requirement applies. Developers who do not publish through Play would use a separate verification route rather than having to create a public Play Store listing.
Identity verification is not the same as a security review of an application. Establishing who controls a developer account can make repeat abuse harder, but it does not prove that every registered application is safe. Nor does it mean that independently distributed software has passed the same review process as a Play Store release.
That distinction matters for users. A verified publisher should not be treated as permission to ignore suspicious payment requests, excessive access privileges or instructions to disable other protections.
Google’s security argument—and the trade-off
Google presented the initiative as a way to make it harder for malicious developers to hide behind disposable identities. Removing one harmful application has limited value if its operator can immediately return under another name. Connecting app registrations to verified developers is intended to raise the cost of that cycle.
The policy targets an accountability gap rather than ending alternative distribution outright. In Google’s stated model, developers can continue choosing where to distribute their applications, but that freedom sits alongside an identity requirement for reaching certified devices.
For independent developers, the concern is the additional dependency this creates. A developer may choose direct distribution precisely to avoid relying on a storefront’s accounts, eligibility decisions or administrative processes. A device-level verification requirement brings Google back into that relationship, even when Google is not hosting the download or processing a purchase.
There are also legitimate reasons for a publisher’s public identity to differ from a legal identity. Small open-source projects may use a collective name. Individual developers may publish under an established pseudonym. Verification, public disclosure and account ownership are separate questions; the details of how each is handled will determine how disruptive the process becomes.
App registration is more than an account form
For engineering teams, Android developer verification introduces work beyond submitting identity information. The developer also needs to establish the relationship between the verified account and the applications it controls.
Two existing Android mechanisms are particularly relevant: package names and app signing keys. A package name identifies an application within Android’s ecosystem, while signing credentials help establish who can issue a trusted update. Registration has to account for that ownership relationship without allowing an unrelated party to claim someone else’s software.
This is why the change deserves attention from release engineers as well as legal or account-administration teams. A company might have several applications maintained by different contractors, signing material held in separate systems and older releases still distributed from a website. Its public brand name alone does not resolve those technical ownership questions.
For teams assessing their exposure, the useful starting point is a distribution inventory:
- Where do installations originate? Separate Play Store releases from website downloads, alternative-store packages and other distribution routes.
- Who controls each application? Identify the organization or individual responsible for the package and its signing credentials.
- Which devices and regions are involved? The announced policy concerns certified devices and a phased geographic rollout, not every Android-derived system at once.
- Which current rules apply? Check Google’s latest documentation for implementation dates, account requirements and any special installation or distribution paths.
These checks are especially relevant to businesses distributing Android apps directly to customers. An installation problem can otherwise look like a broken download, an incompatible handset or an application defect when the underlying issue is an administrative requirement.
Certified Android is the important boundary
Android is both an open-source software project and the foundation of a commercial device ecosystem that includes Google’s services and certification requirements. Those are related, but they are not interchangeable.
The verification announcement concerns certified Android devices. It should not be described as a universal restriction built into every possible Android-based operating system. Equally, describing it as merely a Play Store rule understates its reach: the point of the initiative is to address applications obtained elsewhere.
That boundary explains why the proposal has significance beyond developers already enrolled in Google Play. Alternative app stores and direct-download publishers may retain their own catalogs and customer relationships while still depending on a Google-managed identity layer to reach users on affected devices.
The practical test is whether the system can make impersonation and repeat malicious publishing harder without creating disproportionate obstacles for legitimate independent software. Clear ownership rules, workable account recovery and accessible dispute handling will matter alongside the verification checks themselves.
For now, developers should distinguish the announced rollout timetable from confirmed enforcement on their users’ devices. Google’s official Android developer verification documentation is the primary source for checking current requirements before changing a release process or advising customers that an installation route will stop working.